


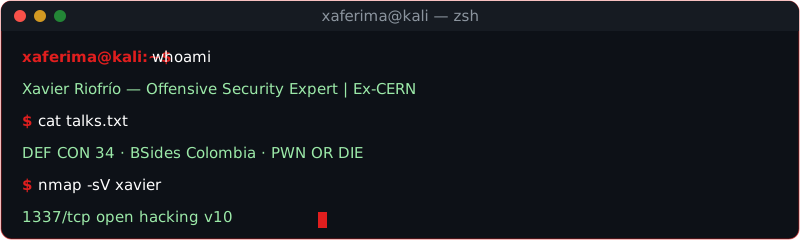
🪪 Offensive Security Expert | Ex-CERN Security Engineer | MSc Cyber Security (Distinction), University of Birmingham
10+ years breaking web, API, mobile & cloud ☁️🔓 Business logic flaws, authN/authZ weaknesses & high-risk flows 🔍 KYC / biometric security research 🧬 Turning findings into remediation that engineering teams actually ship 🛠️


| 🎤 | Event | Talk | Location | Year |
|---|---|---|---|---|
| 🔴 | DEF CON 34 | Your APP Thinks I'm You: A Complete Kill Chain Against Mobile App Security | Las Vegas, USA | 2026 |
| 🔴 | BSides Colombia | Your Brain > Your Toolkit: Real Bugs, Zero Code, Zero Tools | Colombia | 2026 |
| 🔴 | PWN OR DIE | Frustration Kill Chain: un framework para depurar rechazo en seguridad ofensiva | Ecuador | 2026 |
| 🔴 | PWN OR DIE | When Your Mind Becomes the Exploit: No Code, No Tools | Ecuador | 2025 |
| CVE / GHSA | Project | CVSS | CWE | Status |
|---|---|---|---|---|
| CVE-2026-105080 | C4illin/ConvertX v0.18.0 | 9.9 CRITICAL | CWE-94: Improper Control of Generation of Code ("Code Injection") | ✅ Fixed in v0.19.0 |
| GHSA-h2cv-65fq-jgrp · CVE pending | mikefarah/yq ≤4.54.1 | 7.8 HIGH | CWE-78: OS Command Injection | ✅ Fixed in v4.54.2 |
| GHSA-w2hj-54mc-76r4 · CVE pending | pdfcpu/pdfcpu v0.15.0 | 7.5 HIGH | CWE-190: Integer Overflow or Wraparound | ✅ Fixed in v0.16.0 |
| GHSA-9c7h-xjrp-8gh3 · CVE pending | snapotter-hq/SnapOtter ≤ 2.2.0 | 7.1 HIGH | CWE-79: Cross-site Scripting (XSS) | ✅ Fixed in v2.3.0 |
| GHSA-fjh6-rrhv-4g63 · CVE pending | pdfcpu/pdfcpu v0.15.0 | 6.5 MEDIUM | CWE-770: Allocation of Resources Without Limits or Throttling | ✅ Fixed in v0.16.0 |
| GHSA-6524-w46v-6399 · CVE pending | pdfcpu/pdfcpu v0.15.0 | 6.5 MEDIUM | CWE-129: Improper Validation of Array Index | ✅ Fixed in v0.16.1 |
| GHSA-g766-88fx-58h8 · CVE pending | pdfcpu/pdfcpu v0.15.0 | 5.9 MEDIUM | CWE-190: Integer Overflow or Wraparound | ✅ Fixed in v0.16.0 |
6 GHSA advisories published; CVE assignment pending. Technical writeups →


Offensive Security


Mobile & RE


Cloud & Scripting


Environment


AI-Augmented Security


